Originally adapted from The Technology Press. Substantially reviewed and updated 15 September 2026.
The gap is often between the controls
A business may have security software and still have devices nobody manages, accounts with too much access or settings that have drifted away from the intended baseline. Start by finding these gaps, not by buying another product.
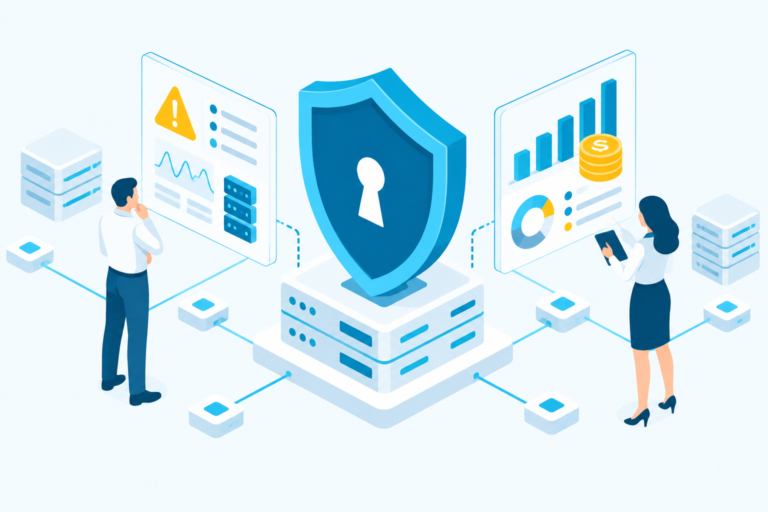
Review the environment as a connected system. A finding needs an owner, a proportionate fix and a check that the fix worked.
Identify exposed assets and access paths.
Asset reviewPrioritise likely business impact.
Risk reviewCheck the control after remediation.
EvidencePractical checkpoints, not a guarantee of security or compliance.
What to check
1. Devices and updates
Find unmanaged endpoints and unsupported software.
What to check
Compare the device inventory with management and protection coverage. Assign exceptions and replacement plans.
2. Access and authentication
Review excess privileges and sign-in methods.
What to check
Remove unnecessary administrator access, review dormant accounts and use phishing-resistant authentication where appropriate. Do not rely on routine password changes as the main defence.
3. Configuration and response
Check network paths, settings and reporting.
What to check
Review segmentation and configuration changes, then make sure staff know how to report suspicious requests promptly. These are three separate checks, not a single software setting.
Sources & further reading
Make the next step practical
Talk to ITFR about your business, priorities and the controls that fit.